Products · Security
Next-Generation Firewall and network security
Perimeter protection, segmentation into security zones, secured remote access, intrusion detection and prevention. NGFW features, VPN, MFA and rule management for the secure operation of modern networks, open-source based.
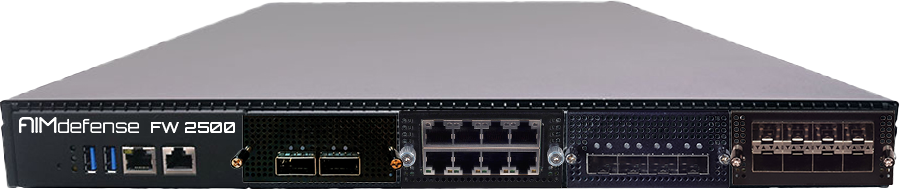
Security functions
Protection from the network edge into the zones
Five functional areas for the controlled, transparent operation of modern networks. Implemented with the AIMdefense next-generation firewall, either dedicated on an appliance or virtualised.
Perimeter & firewalling
- Stateful firewalling (Layer 3/4)
- NGFW features (Layer 7), app/protocol filtering
- NAT, site-to-site and client VPN
Segmentation & zones
- VLAN-based zones (client, server, DMZ)
- Inter-zone firewalling, east-west control
- Least privilege, smaller attack surface
Remote access & access control
- Site-to-site and client VPN
- Multi-factor authentication (MFA)
- Role-based access control, logging
Intrusion detection & prevention
- IDS and IPS, signature-based
- Blocking of suspicious traffic
- Protection against known exploits
Security in operation
- Rule and policy maintenance, change safety
- Update and patch strategies
- Logging, audit and compliance readiness
AIMdefense: the next-generation firewall for your appliance.
Open-source based and vendor-independent, as a bookable option for the matching AIMSTRONG hardware. Segmentation, MFA, IDS/IPS and audit-proof logging are at the same time core NIS2 building blocks.
Straight from the shop
AIMdefense, straight from the shop
Security options for the matching appliance, with up-to-date prices.
Orientation
Which security function do you need?
From the firewall to attack detection, here is the right match.
Which firewall functions do I get?+−
How do I segment my network?+−
Secure remote access and MFA?+−
Detecting and preventing attacks?+−
Does this run on my own hardware?+−
How does this help with NIS2?+−
Security functions for the matching appliance, in the shop.
Options and classes in the shop, or have a quick chat if you would like to align on the right combination.