Skip to Content

Products · Overview

Network and IT security without vendor lock-in

Firewall appliances, next-generation firewall and central network management from a single source. Vendor-independent, open-source based and made in Germany. NIS2-ready, with support and RMA from Germany.
Next-Generation FirewallOPNsense / pfSensevendor-independentNIS2 & KRITISMade in Germany
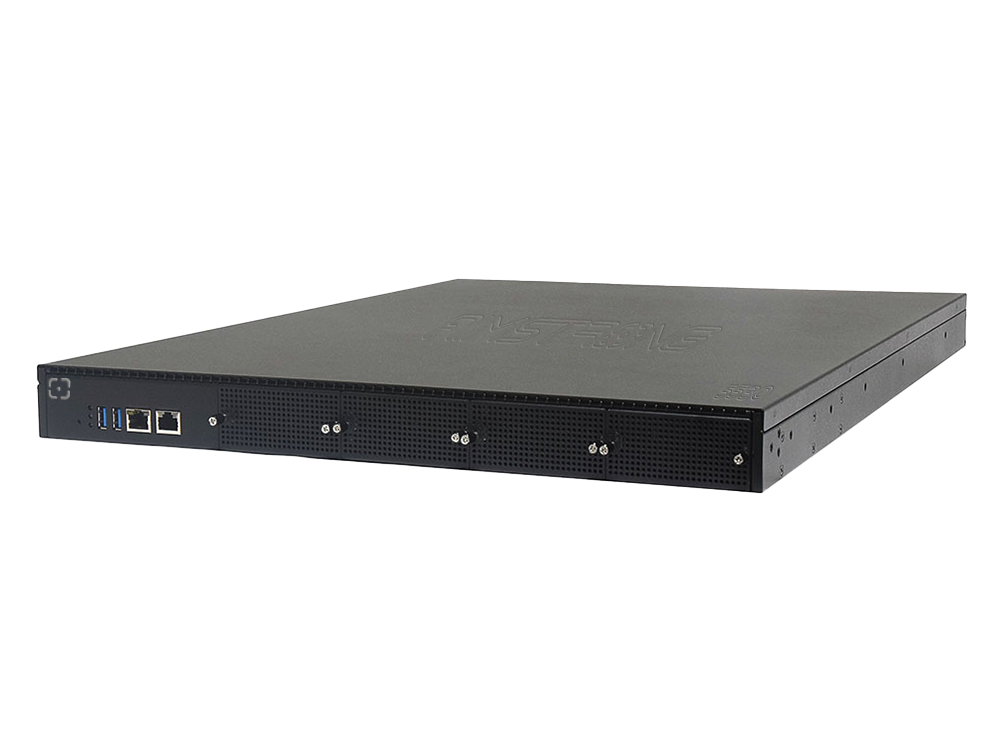
Network appliance / firewall appliance in rack format

From a single source

Hardware, security and management, modularly combined

Three building blocks that fit together but work on their own. You choose the hardware, the firewall and the management, without tying yourself to a single vendor.

Network appliances & hardware

  • x86 firewall appliances, desktop to rackmount
  • Managed switching & routing (L2/L3, SFP+, 10GbE)
  • Edge, thin-client and data-centre systems
All hardware details →

Next-Generation Firewall

  • NGFW, perimeter and gateway protection
  • Segmentation, VPN, IDS/IPS, MFA
  • Open-source base, as an option to the appliance
All security details →

Central management

  • One interface for all sites
  • Monitoring, backup, NAC, automation
  • Multi-tenant, cross-vendor
All management details →

The portfolio is designed to be open: further technology partners and products can be added at any time.

NIS2 & KRITIS

NIS2 sets the checklist. We deliver it.

From 2026, NIS2 obliges around 30,000 companies in Germany to take concrete security measures, with personal responsibility for management. It sounds like effort, but above all it is a clear list. Our portfolio covers it technically, from a single source and with data in Germany.

Network security & segmentation
Next-generation firewall and managed switching for isolated security zones.
Detect incidents & report within 24 h
Central monitoring with alerts and audit-proof reporting.
Access control & MFA
Two-factor authentication and network access control (NAC).
Backup & business continuity
Centrally managed backups with cycles, templates and jump host.
Evidence & documentation
Automatic reports and analyses as proof of compliance.
Risk analysis & vulnerabilities
Vulnerability analysis with a risk-sorted report as a starting point.

Note: not legal advice. Whether and how NIS2 applies to you specifically, we assess together with our legal partner. As of 2026.

Straight from the shop

Firewall appliances, available now

A current selection with up-to-date prices straight from the shop.

Your dynamic snippet will appear here ... This message is shown because you have provided neither a filter nor a template to use.

Central management

One interface. All sites.

Network topology, access control, backups and maintenance in a web-based, multi-tenant platform. Either on the appliance or vendor-independent, ideal for IT departments and system houses.
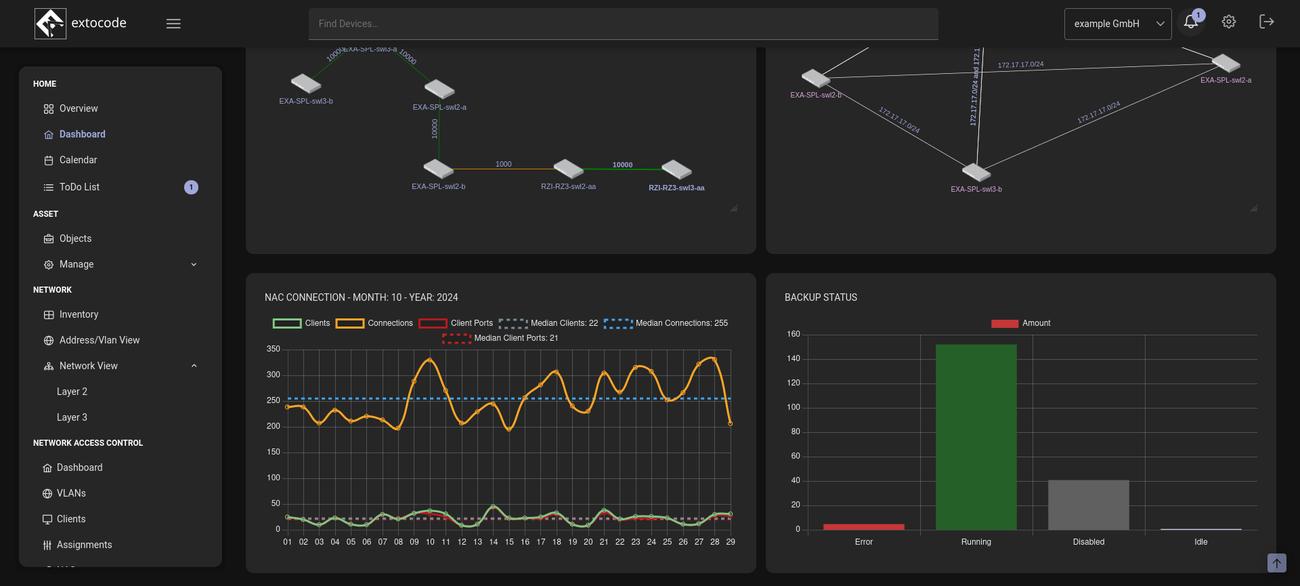
  • Layer 2/3 topology, real-time traffic and PoE status
  • NAC, backup, hypervisor and captive-portal modules
  • Multi-tenant, roles/rights, maintenance calendar
Central network management dashboard with topology, NAC and backup status

Typical requirements

What task is on your desk?

Secure the perimeter, connect sites via VPN
→ Next-generation firewall on a suitable appliance, with segmentation and remote access.
Robust, structured network hardware
→ Managed switching & routing, L2/L3, SFP+/10GbE, PoE.
Compact, reliable systems for edge and office
→ Fan-less desktop appliances and thin clients.
Monitor and manage all sites centrally
→ Central management with monitoring, backup and NAC.
Highly available and fail-safe
→ Rackmount systems with redundancy and scale-out.
Meet and prove NIS2 requirements
→ Portfolio + reporting along the NIS2 checklist.

Orientation

Which product fits your needs?

Our product names are new, the tasks are not. Here is the right match.

I need a firewall for a single site or a small network.+−
AIMSTRONG-1040AIMSTRONG-1515 Compact, fan-less desktop appliances with the next-generation firewall of your choice (OPNsense, pfSense or our security option). Lean rather than bloated, productive in minutes.
I need firewall performance for the data centre or many sites.+−
AIMSTRONG-2512 to 5530 Rackmount appliances with 10G SFP+, redundancy and scale-out. For high throughput and high availability.
I want to manage all sites from a single interface.+−
Central management A web-based, multi-tenant platform: topology, monitoring, backup, NAC and maintenance. Either on the appliance or vendor-independent.
I need managed switching or routing.+−
AIMnetworksAIMroute Managed switches and routers (L2/L3, SFP+, PoE) that fit into the same central management.
I do not want forced hardware and prefer open source.+−
Every appliance runs OPNsense, pfSense or our open-source-based security option. No vendor lock-in, full control, German support and RMA.
How does this help me with NIS2 in practice?+−
Firewall/segmentation, monitoring & reporting, MFA/NAC and backup cover the core NIS2 requirements technically, with audit-proof documentation. The legal assessment is handled together with our legal partner.

Ready? You will find everything available in the shop.

Order directly, or have a quick chat if you would like to align on the right appliance class.